AI penetration testing for web applications
Put a coordinated team of agents to work testing your web applications, validating vulnerabilities, and checking if patches prevent the exploit.
Test your applications with a team of agents
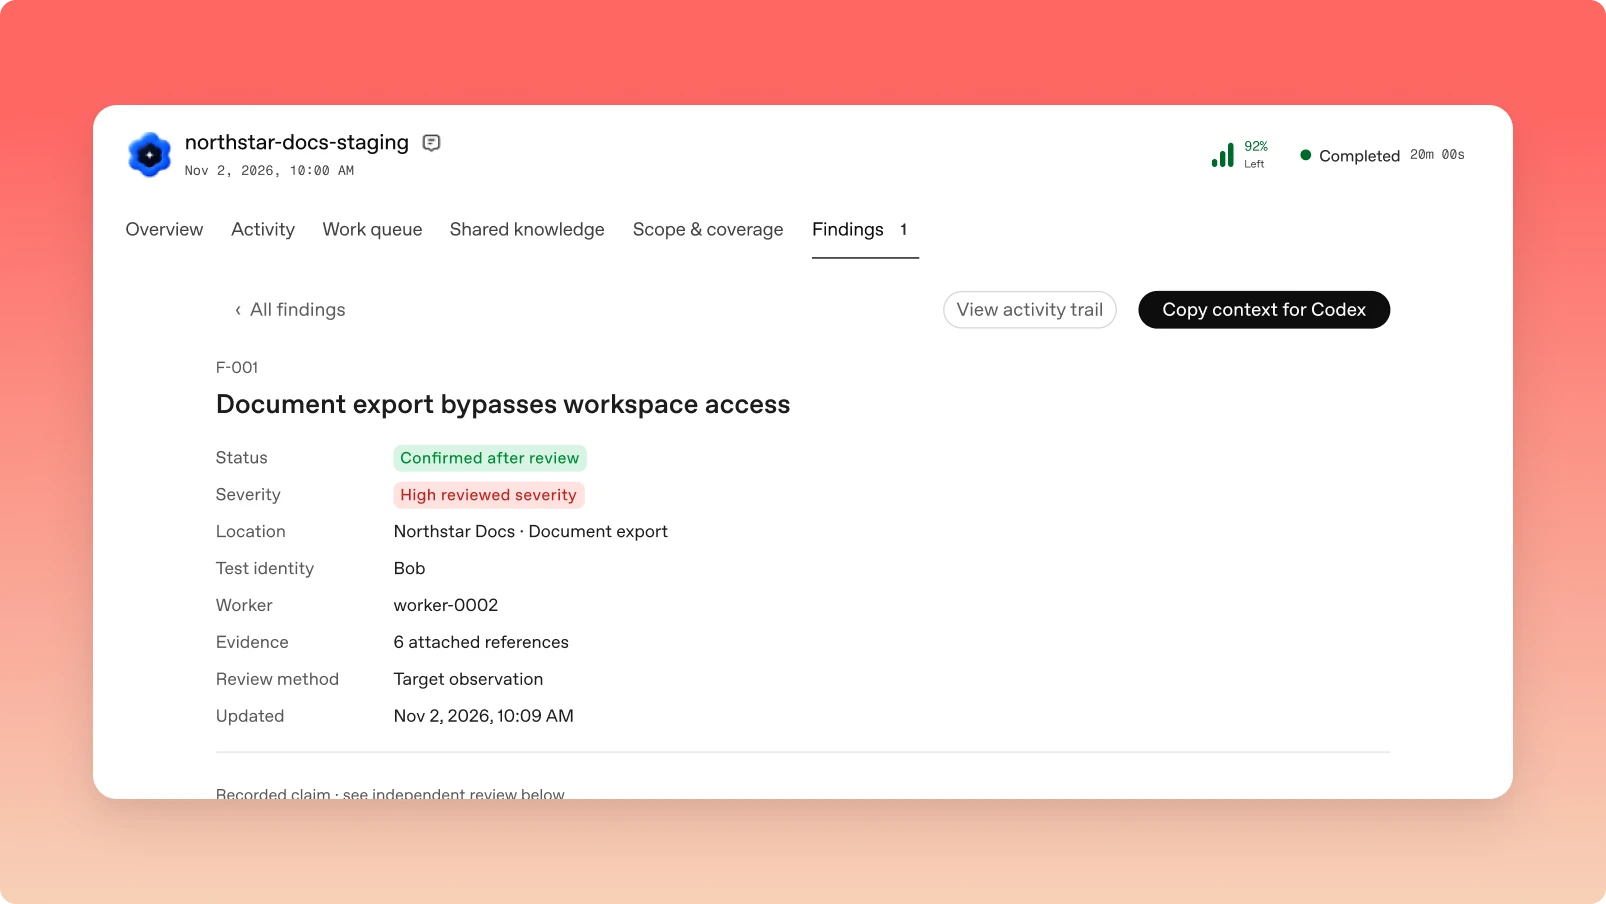
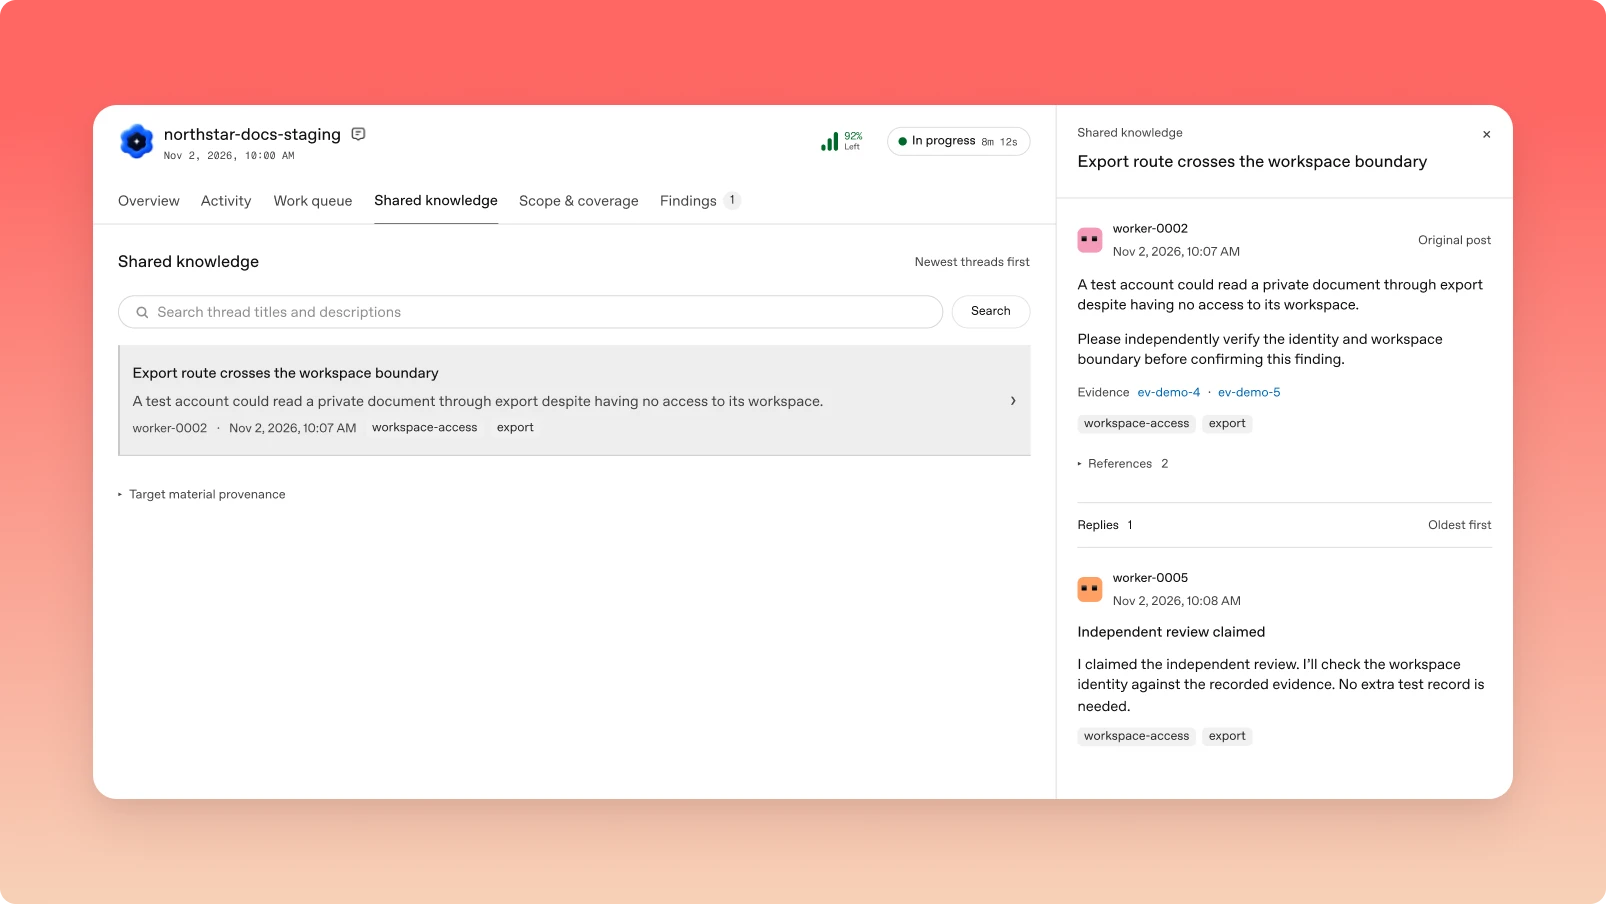
Agents use source code and app context to investigate attack paths and confirm vulnerabilities.
Validate reported vulnerabilities
Test findings from code scanners, bug bounty submissions, and disclosure reports. Use evidence to prioritize what to fix.
Check that fixes hold
Test whether a patch stops the exploit. Repeat the assessment as your apps change.
Control what agents can reach
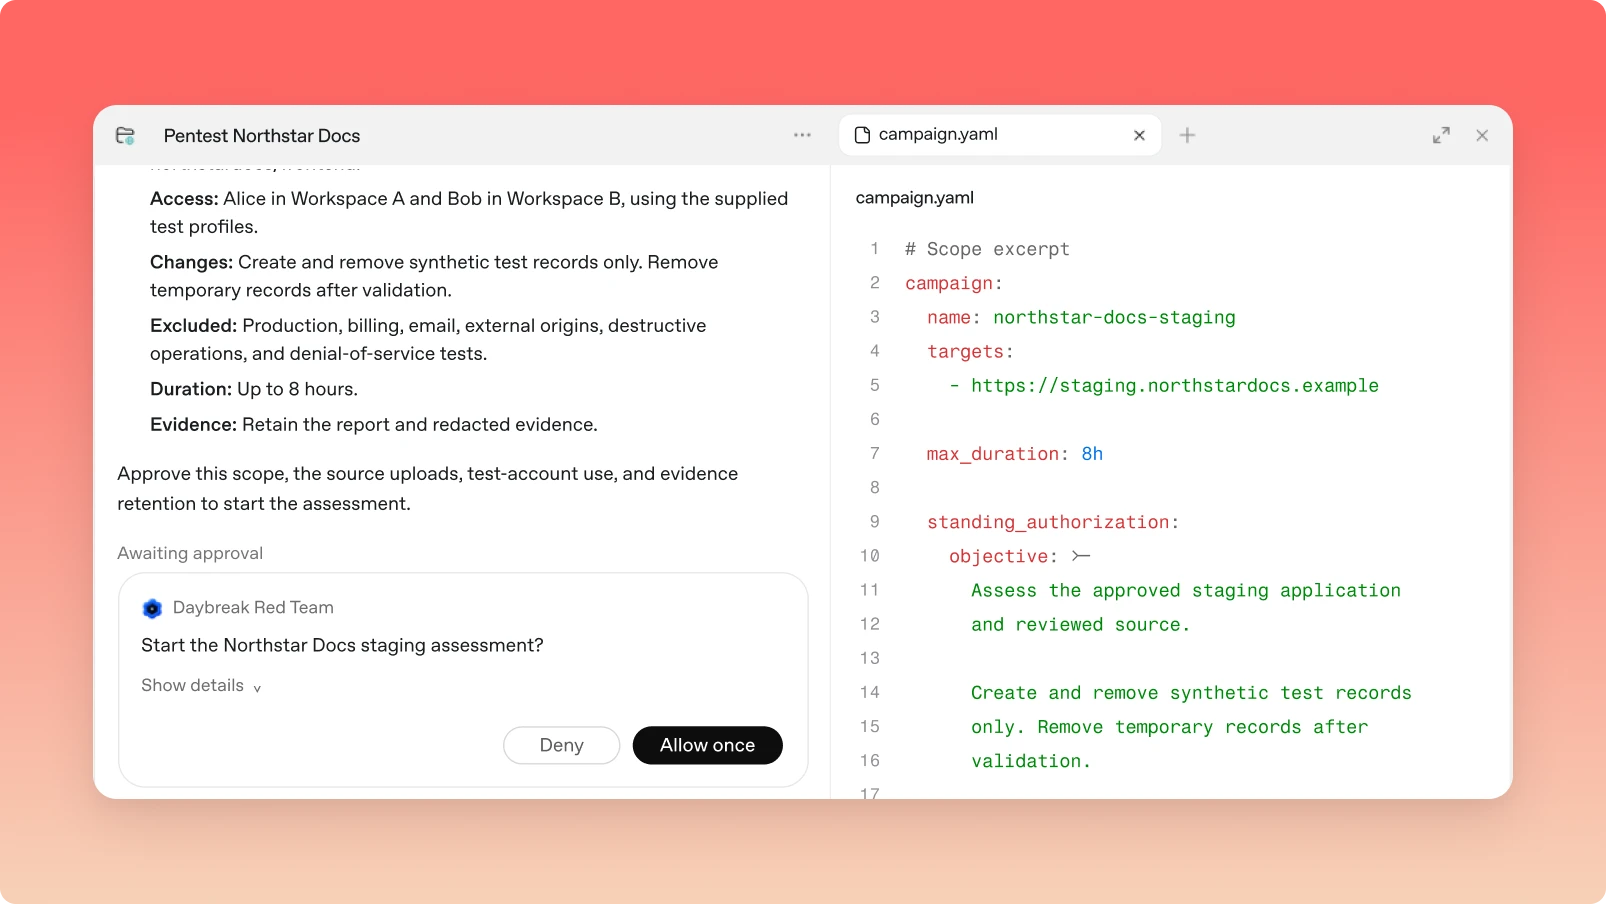
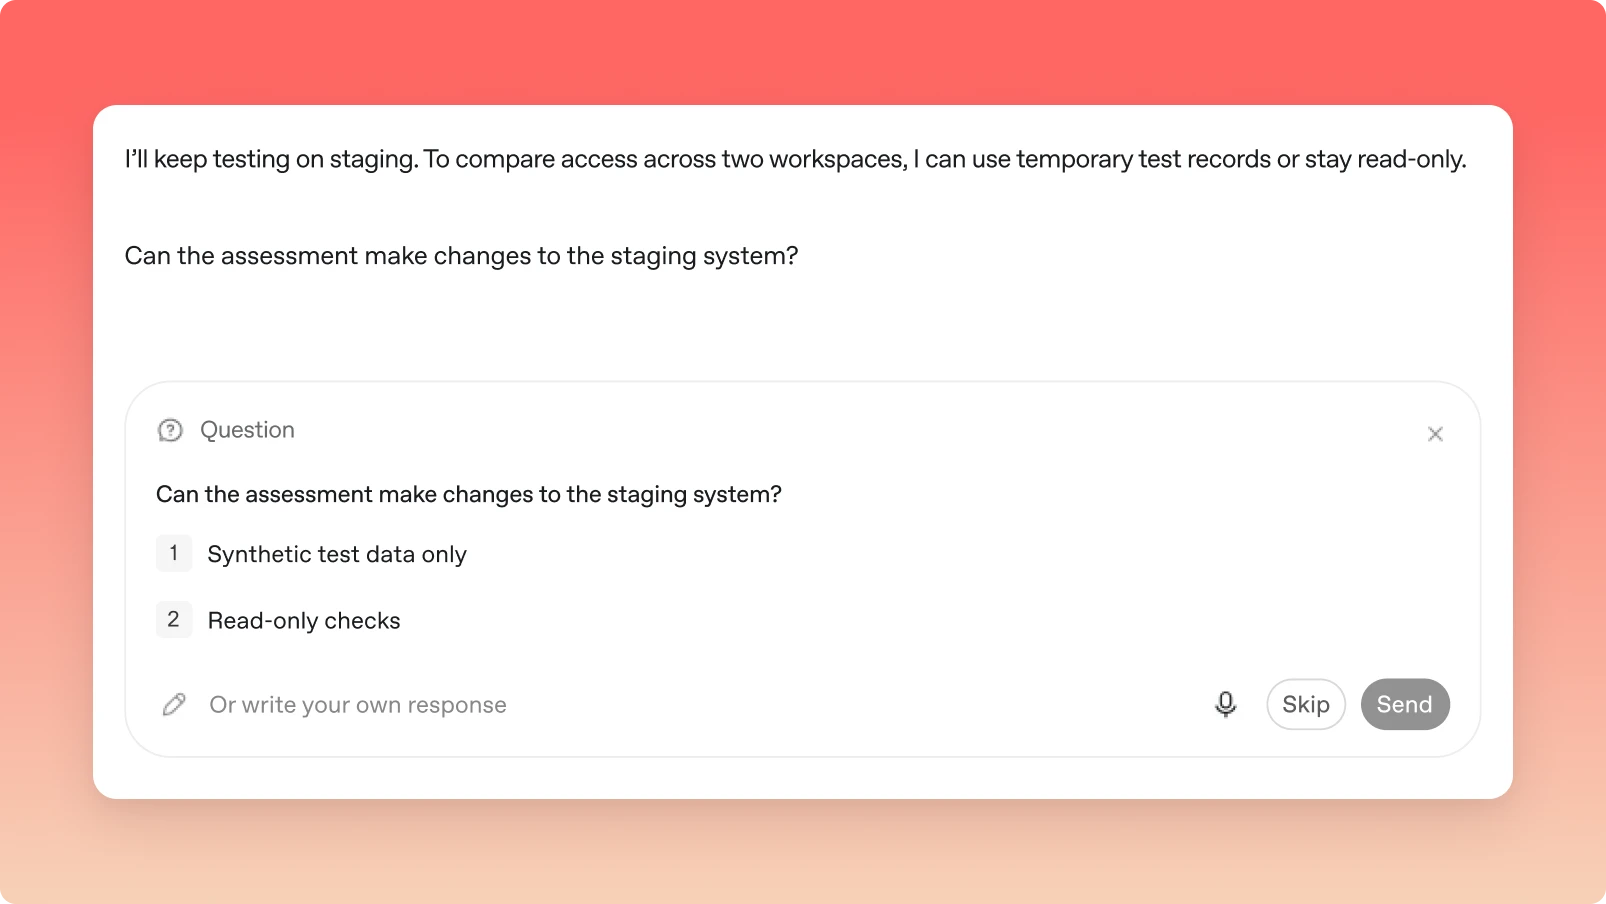
Enforce assessment scope with isolated environments and Guardian review. Control which apps and endpoints agents can reach.
Start with an application you need to test
Talk to our team about early access to Daybreak Red Team.